Internal Audit Workflow Automation
From client data to partner-ready observations, in one automated workflow
Internal Audit bryk is an AI-native workflow for CA and audit firms. It brings data requests, audit programs and risk control matrices together, checks what your clients upload, tests every audit step, and drafts observations for your partners to review and finalize.
Does your Internal audit still run on email and spreadsheets?
Every engagement starts the same way, and loses time the same way. Data requests are chased over email and WhatsApp. Files are opened one by one to check whether they are the right ones. Audit steps, risks and controls sit in separate sheets, so no one is sure what is actually covered. Observations are written at the end, under deadline pressure. Partners review late, juniors rework, and quality depends on who is on the engagement.
bryks ai Internal Audit automates the workflow from data to observations
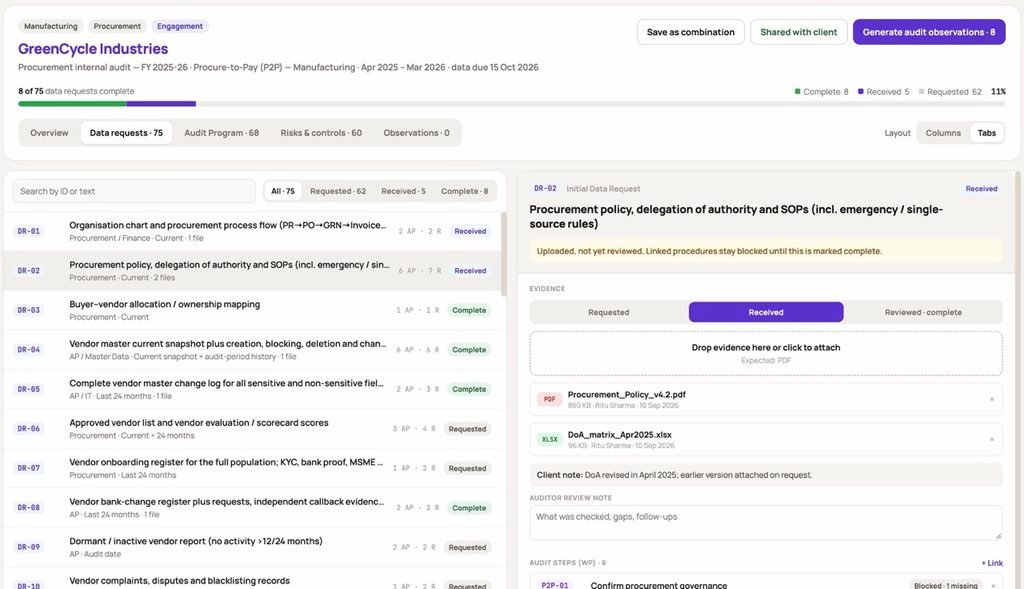
- Start from a template: Choose the industry and process. You get the data request list, the audit program and the risk control matrix, already linked to each other.
- Clients upload against each request: Share the request list with your client. They upload files against each item and can see what is pending, submitted or accepted.
- AI validation: Each upload is checked for the right document, the right period and completeness. Problems are caught early, before your team spends time on them.
- AI tests every audit step: Once the data is in, each line of the audit program is tested against it, using the sampling approach and exception criteria in your program.
- AI cross-checks risks and controls: Results are read across the risk control matrix to show whether each risk is handled by a control that is working, and where there are gaps.
- AI drafts observations, partners decide: When the evidence is squared off, observations are drafted with their supporting references. Your partner reviews, edits and finalizes.
Templates built for your industry and process
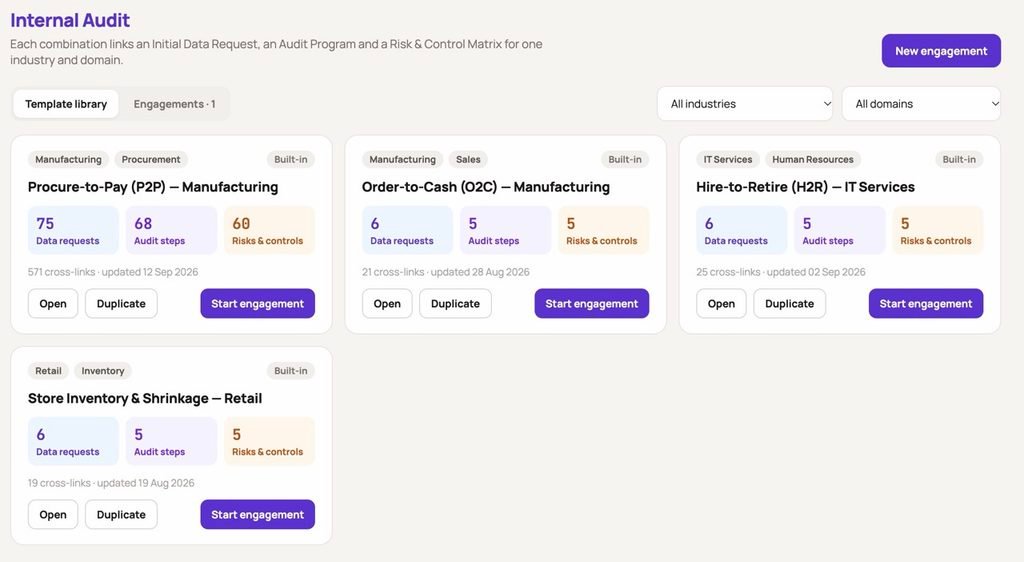
Start with a complete set, not a blank sheet. Each template combines three things: the data requests to send, the audit steps to perform, and the risks and controls to assess. Every data request is linked to the audit steps and risks it supports. Our sample library includes:
- Procure-to-pay for manufacturing: 75 data requests, 68 audit steps and 60 risks and controls.
- Order-to-cash for manufacturing.
- Hire-to-retire for IT services.
- Store inventory and shrinkage for retail.
These are samples. We build libraries for any industry or process, based on what your clients need. You can also copy any template, adapt it to your firm’s methodology and save it as your own.
Know where every risk stands
Internal Assessment shows each risk alongside its control and the audit steps that test it.
- Which audit steps are blocked waiting for data, ready to test, or finished.
- Which steps found exceptions, and which found none.
- Which risks are fully tested, partly tested or not yet covered.
- Design and operating effectiveness for each control, with residual risk noted.
You see the gaps before the partner asks, not after the report is drafted.
Observations partners can sign off with confidence
Each observation is drafted in a standard structure that management can act on:
- Condition and criteria
- Risk and impact
- Root cause
- Recommendation and management action
- Owner, due date, priority and financial exposure
Every observation links back to the data request, audit step and risk it came from, so anyone reviewing can trace it to the evidence. Export the full list when you are ready to share. AI does the reading, testing and first draft. Your people apply the judgement. AI-drafted observations are marked as drafts until reviewed, and every field can be edited. Partners can follow each observation from Draft to Open, Agreed with management and Closed.
Client data confidentiality
- Confidential client files are kept in a dedicated, isolated storage environment of your own, not mixed with data from bryks.ai or other clients.
- For regulated work, deploy fully on-premises or in your own cloud.
- You and your clients own your data and institutional knowledge. bryks.ai does not.
Who is it for?
- CA and audit firms: Firms that deliver internal audit for multiple clients and want consistent quality across engagements.
- Partners: Partners who want to review sooner, with evidence in front of them.
- Growing practices: Teams that want to take on more client work without adding headcount in the same proportion.
- In-house audit teams: Internal audit functions that want a connected workflow instead of scattered files.
Frequently asked questions
- Does the AI replace the auditor’s judgement? No. AI reads files, runs tests and drafts observations. Partners and managers review, edit and decide what goes to the client.
- Can we use our own audit programs and risk control matrices? Yes. Copy any template, adapt it to your methodology and save it for future engagements. We can also build new libraries for any industry.
- Which industries are covered? The sample library covers manufacturing, IT services and retail. We add industries and processes based on what your clients need.
- Where is client data stored, and who owns it? Client files are kept in a dedicated, isolated environment, or fully inside your own cloud or on-premises setup for regulated work. The data belongs to you and your clients.
- What do our clients need to do? Open their request list, upload files against each item and track what has been accepted. They see only their own engagement.